Tech
Massive Data Breaches Hit Airports and Driver’s License SystemsSecurity incidents are piling up
Massive cyberattacks targeting airports, driver’s license systems and websites highlight the growing scale of AI-era cybersecurity threats.

The Driver’s License Mega-Breach — IDScan.net
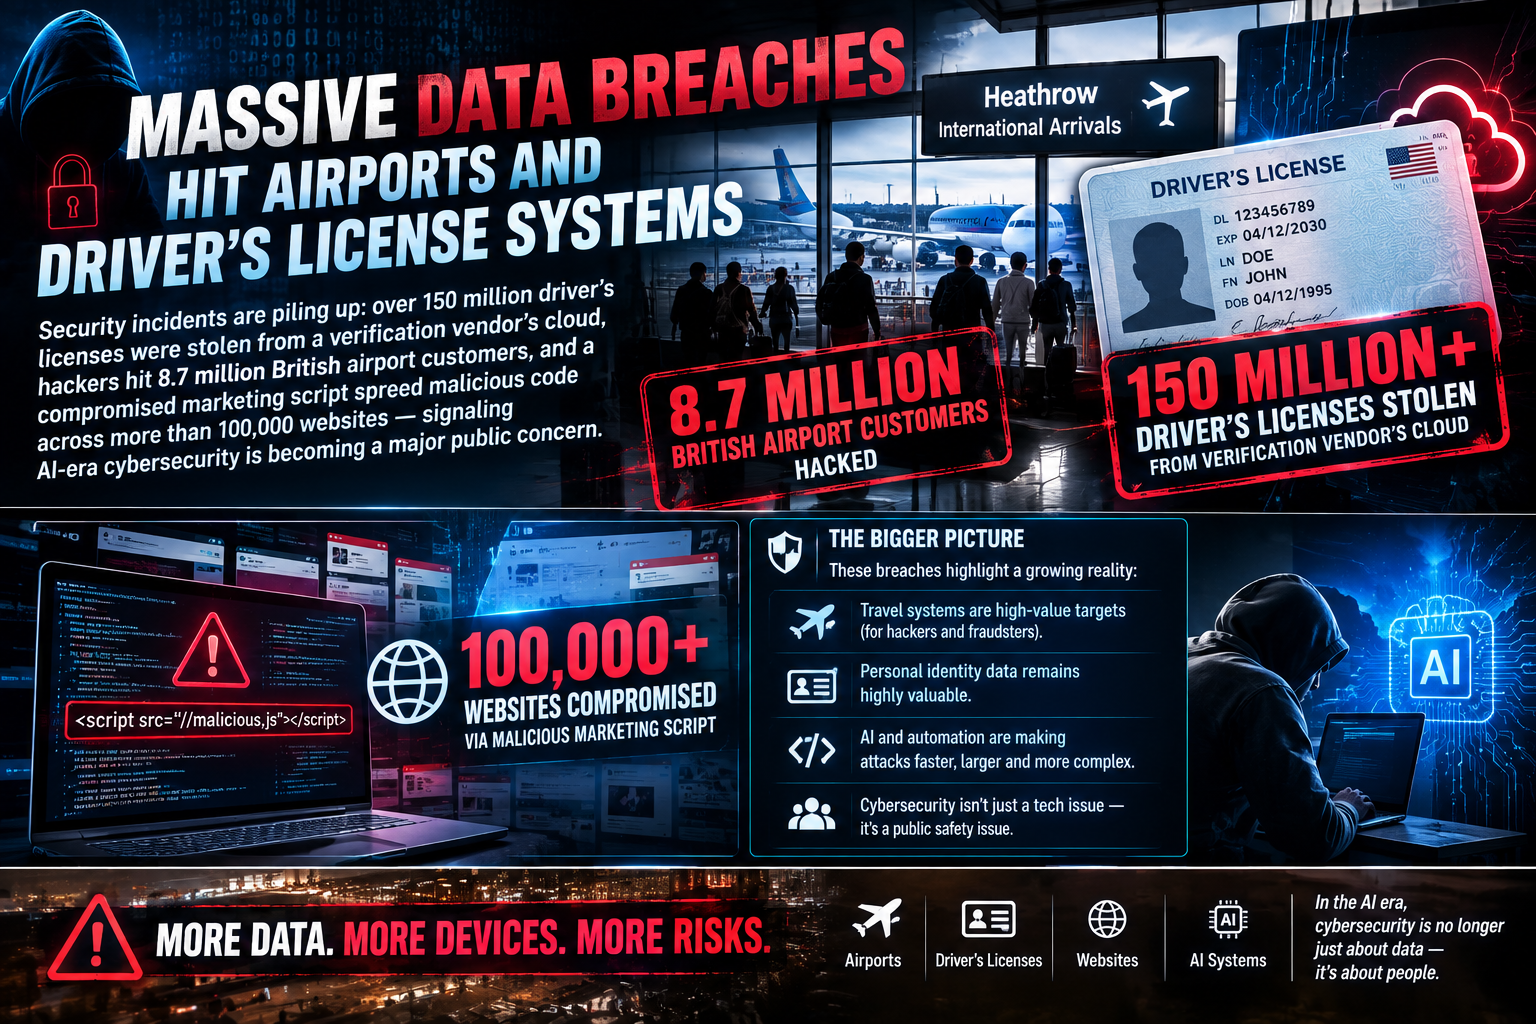
What happened: A dark web marketplace called “Nexus,” run in Russian-language cybercrime forums, offered buyers searchable access to more than 153 million U.S. and Canadian driver’s licenses, over 10 million ID cards, more than 3 million travel documents, and roughly 579,000 medical cards. Independent cybersecurity journalist Brian Krebs discovered the marketplace, verified it by finding his own scanned driver’s license in the database, and confirmed the leak with several other individuals he contacted.
How long it went undetected: IDScan later disclosed to Illinois’ attorney general that hackers had access to its systems for at least five months, between April 1 and September 2, 2026. The listing had reportedly been growing by around 400,000 new records every 24 hours before the service abruptly went dark on September 2.
The company’s response: IDScan confirmed on September 4 that “an unauthorized third party may have accessed and/or copied certain customer information” stored in its IDScan.net cloud platform — including full names, driver’s license numbers, and identification numbers from other government documents like passports. IDScan is used by corporate clients ranging from entertainment venues to cannabis dispensaries to verify customer identity documents, meaning the exposure likely spans all 50 US states.
Notable detail: Reports indicate the breach even affected high-profile individuals, with one database entry reportedly belonging to US Defense Secretary Pete Hegseth.
Why it’s being called a national security issue, not just a consumer breach: National security outlet Lawfare published an analysis on September 14 arguing this breach belongs in the same category as OPM, Equifax, and Anthem — because it combines durable identifiers (names, license numbers) with verified real faces, giving foreign intelligence services a tool to potentially unmask undercover officers, track diplomats, and build detailed profiles of American officials.
FBI involvement: The FBI is now investigating alongside IDScan itself.
2. Manchester Airports Group — 8.7 Million UK Airport Customers
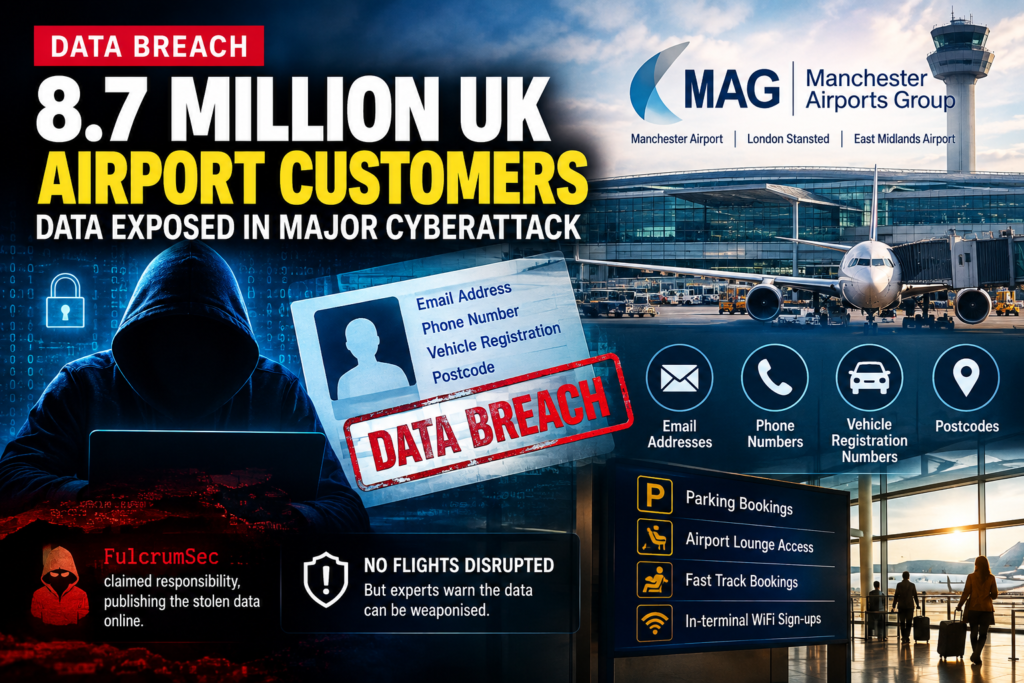
What happened: Manchester Airports Group (MAG) — which operates Manchester Airport, London Stansted, and East Midlands Airport, serving roughly 65 million passengers a year — confirmed on August 27 that an “unauthorized third party” accessed customer data belonging to approximately 8.7 million people (one source puts it at 8.8 million).
What was taken: Data tied to parking bookings, airport lounge access, Fast Track security bookings, and in-terminal WiFi sign-ups — specifically email addresses, phone numbers, vehicle registration numbers, and postcodes. No bank details or payment card information was exposed.
Extortion angle: According to BBC News, attackers demanded a ransom, which MAG refused to pay — and a hacking group calling itself FulcrumSec later claimed responsibility, subsequently publishing the stolen email addresses and phone numbers online.
Safety reassurance: MAG stressed that flight operations and passenger safety were never disrupted, and no group has been officially, definitively linked to the attack by investigators.
Pattern with prior aviation attacks: This is the second major cyberattack to hit UK/European aviation infrastructure in under a year, following the September 2025 ransomware attack on Collins Aerospace’s check-in software that grounded systems at Heathrow, Brussels, and Berlin. The pattern experts are flagging: airports keep getting hit not through flight-critical systems, but through ancillary software — parking, lounge bookings, WiFi sign-ups — suggesting the industry’s weakest security links are its peripheral consumer-facing tools rather than core operations.
Expert warning: Graeme Stewart of Check Point Software cautioned: “The absence of cancelled flights or queues at terminals does not make this a small cyber attack. The data reportedly taken can now be weaponised” — for example, to craft convincing fake parking refund scams or fraudulent Fast Track service communications.
3. The Brevo Supply-Chain Attack — 100,000+ Websites
What happened: Brevo (formerly Sendinblue), a widely used marketing/CRM platform, suffered a two-stage attack:
- September 10: Attackers exploited a vulnerability in Brevo’s SAML SSO (single sign-on) system to access 138 customer accounts — including one belonging to cryptocurrency storage provider Trezor — and used six of those accounts to send phishing emails, plus exported contact lists from 43 accounts.
- September 14: After Brevo closed that initial breach, attackers returned using a compromised, long-lived Cloudflare API key to deploy a malicious “Cloudflare Worker” that injected harmful scripts directly into Brevo’s own website and into three JavaScript files that Brevo customers embed on their own sites (covering forms, a chat widget, and an SDK loader).
The attack window: The malicious code was live for roughly five and a half hours on September 14 (16:05 to 20:13 UTC), reaching an estimated 100,000+ customer websites, according to cybersecurity firm Sansec.
What visitors experienced — “ClickFix” social engineering: Ordinary site visitors saw a fake “verify you are human” Cloudflare-style prompt instructing them to press Win+R, then Ctrl+V, then Enter — a technique that tricks people into personally executing a malicious command that had been secretly copied to their clipboard, downloading malware onto their machine. This bypasses traditional browser security because the victim runs the malicious code themselves.
The bigger threat for site owners — WordPress admin backdoors: For visitors who happened to be logged in as WordPress administrators, the script instead quietly attempted to install a malicious plugin — creating a lasting, persistent backdoor into the website itself, independent of the original attack window.
Resolution: Brevo revoked the compromised credentials and removed the malicious worker; all malicious subdomains stopped resolving by September 15.
Why This Trio of Stories Matters Together
All three incidents in the same window illustrate the same underlying pattern experts are increasingly worried about: it’s not the big tech giants or AI labs getting hit directly — it’s the third-party vendors and supply chains everyone quietly depends on (an ID verification company, an airport’s parking/WiFi vendor, a marketing platform’s embedded scripts). One analysis captured it well: vendor-level infrastructure, not just the AI labs themselves, is where a growing share of 2026’s security incidents are actually originating.






Tech
Indian equity markets swing on IT-sector drag vs. broader gainsSensex and Nifty opened higher today
Indian markets opened higher, but IT stocks slipped amid H-1B fee concerns while consumer and auto stocks supported broader gains.

Tech
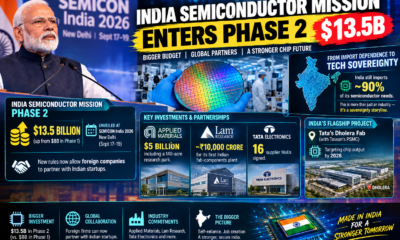
India Semiconductor Mission enters Phase 2 ($13.5B)At SEMICON India 2026 in New Delhi
India launches Semiconductor Mission Phase 2 with $13.5 billion in funding and major global investments to strengthen domestic chip manufacturing.
The Official Numbers
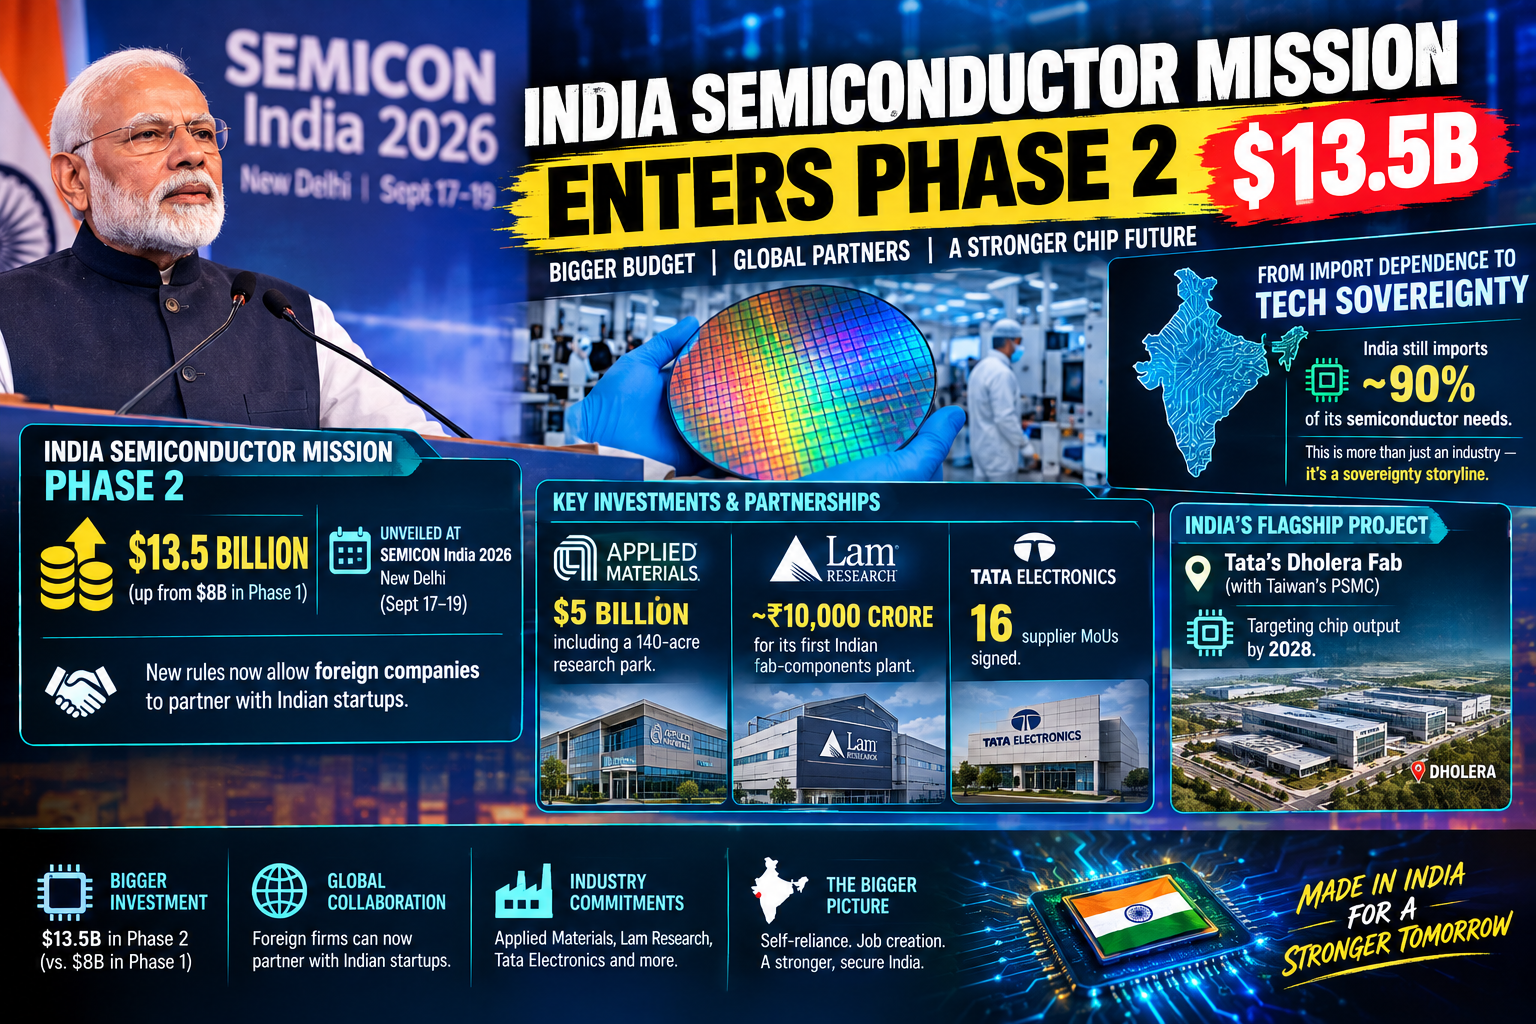
The Union Cabinet approved Semicon 2.0 on July 15, 2026, with a fiscal outlay of ₹1,27,500 crore (~$13.5–15 billion depending on the source and exchange rate used) — up from Phase 1’s ₹76,000 crore (~$8 billion). Gazette notifications for the scheme were issued August 31, and guidelines for all six strategic pillars were released just before the SEMICON India 2026 event opened.
Semicon 1.0 by the numbers: the original ₹76,000 crore outlay is now almost fully committed — ₹64,000 crore went to chip fabs, ₹10,000 crore to the semiconductor lab, and ₹1,000 crore to the Design-Linked Incentive scheme. As of December 2025, 10 projects had been approved with a combined investment of over ₹1.6 lakh crore, spread across six states: Gujarat, Assam, Uttar Pradesh, Punjab, Odisha, and Andhra Pradesh.
The Event Itself
SEMICON India 2026 ran September 17–19 at Yashobhoomi (IICC), New Delhi, under the theme “Business Opportunities Await” / “Silicon to Systems: Building the Ecosystem.” It drew 535 exhibiting companies — up 52% from 351 in 2025 and nearly double 2024’s 271 — with the sharpest growth notably not in chipmakers themselves, but in the companies that fabs buy from once construction gets real: cleanroom and utility contractors, specialty gas and chemical suppliers, and metrology/inspection tool vendors. That shift is being read as a signal India’s chip push has moved from announcements into actual procurement.
What Modi Actually Said
Framing India as a “trusted manufacturing destination” amid global supply-chain diversification, Modi called on companies to strengthen capabilities across the entire value chain — design, equipment, materials, testing, and packaging — and specifically appealed to Indian researchers working abroad to “join the development of advanced technologies in India.” He also pointed to new regulatory changes enabling partnerships between global companies, Indian startups, and design houses — a notable opening for foreign firms to plug directly into India’s smaller domestic players rather than only building their own standalone facilities.
The Big Corporate Commitments
Applied Materials — “India Vision 2035” ($5 billion)
Announced by executive Prabhu Raja, this includes a planned 140-acre research park plus broader investment across research, equipment components, and materials over roughly a decade — one of the most significant single commitments of the show.
Lam Research (~₹10,000 crore)
Its first Indian manufacturing plan, focused on silicon components — a materially different bet than assembling finished tools, since it puts actual component manufacturing (not just R&D or sales) onshore.
Fujifilm (~₹800 crore)
A separate materials-facility investment, adding to the growing “supply chain around the fabs” story.
Tata Electronics — 16 MoUs
CEO Randhir Thakur announced Tata would sign 16 memoranda of understanding during the event, with partners including Nexperia, BESI, JSR, Fujifilm, L&T Semiconductors, and Inox Air Products — spanning fabrication, packaging, materials, cleanroom infrastructure, design, and workforce development, tied to the Gujarat and Assam projects specifically.
The Flagship Project: Tata’s Dholera Fab
This remains the centerpiece of India’s entire chip ambition:
- A 300mm (12-inch), AI-enabled fabrication facility built with Taiwan’s Powerchip Semiconductor Manufacturing Corp (PSMC)
- Targeting 50,000 wafer starts per month at 28nm–110nm process nodes — covering automotive chips, industrial microcontrollers, AI accelerators, IoT devices, and display drivers
- Total investment: ₹91,000 crore (Dholera fab) — Tata’s combined outlay for Dholera plus its Assam (Jagiroad) packaging facility is ₹1.18 lakh crore, with the government covering 50% of eligible capex on a pari-passu basis
- Thakur said Tata has brought together more than 450 ecosystem partners just for Dholera’s construction, equipment, chemicals, and materials needs
- Separately, Tata has also partnered with Dutch lithography giant ASML on technology, training, and supply-chain development
- Tata says both Dholera and the Assam packaging plant are on schedule, with the combined projects expected to generate nearly 50,000 direct and indirect jobs. Company-wide, Tata Electronics says it has already created over 150,000 direct jobs, with 65% of its workforce being women, including from rural and marginalized communities

Other Notable Progress Already on the Ground
This isn’t purely future-tense — some projects are already shipping:
- Kaynes Semicon’s OSAT unit in Sanand reached commercial production in March 2026, just 14 months after breaking ground, and shipped India’s first commercially produced multi-chip modules (900 units) to Alpha & Omega Semiconductor back in October 2025 — with plans to scale to 6.3 million chips per day
- Micron’s Sanand assembly/test facility ($2.75 billion) is also under construction, using the same contractor (Tata Projects) as the Dholera fab
- CG Semi’s OSAT facility in Sanand was inaugurated by Modi on July 4, 2026
- India is also pushing toward more advanced nodes: officials have said the roadmap moves from current 28nm capability toward 5–7nm chip manufacturing over time, to close the gap with global leaders
The “Sovereignty” Framing — Why It Matters
India currently imports roughly 90% of its semiconductor needs, and the domestic market is projected to be worth over $100 billion by 2030, with the broader ecosystem potentially adding 600,000 jobs. Given semiconductors’ role in everything from smartphones to defense electronics to AI infrastructure, ISM Phase 2 is being pitched less as an industrial policy story and more as a strategic autonomy story — reducing reliance on Taiwan, China, and the US amid a period of heightened global chip-supply nationalism (a theme that connects directly to your earlier segments on US-China chip tensions and Nvidia/OpenAI/Google’s custom silicon race).
Tech
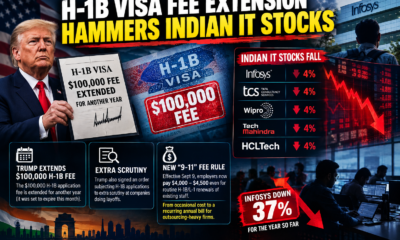
H-1B visa fee extension hammers Indian IT stocks
Trump’s H-1B fee extension sends Indian IT stocks lower as companies face higher visa costs, added scrutiny and recurring renewal expenses.

The Timeline — This Has Been Building Since Last Year
- September 2025: Trump first imposed the $100,000 H-1B fee, with only a one-day implementation window (anyone entering the US after 12:01am Sept 21, 2025 was covered) — Nasscom called this deadline “unrealistic and disruptive.” Indian IT stocks lost ₹85,500 crore in market cap in a single day on that original announcement, with the Nifty IT index falling nearly 3%.
- December 2025: A US federal judge upheld the fee as lawful.
- June 2026: A different federal judge — District Judge Leo Sorokin — struck it down, ruling bluntly that “the President had no power or delegated authority to impose a tax on H-1B petitions.” That ruling was stayed pending appeal, so the fee kept operating anyway.
- August 25, 2026: The administration formally proposed codifying the fee as a $103,265 regulation.
- September 18–19, 2026: Trump signed a new proclamation extending the restrictions for another 12 months, through September 21, 2027.
The Numbers That Matter for India Specifically
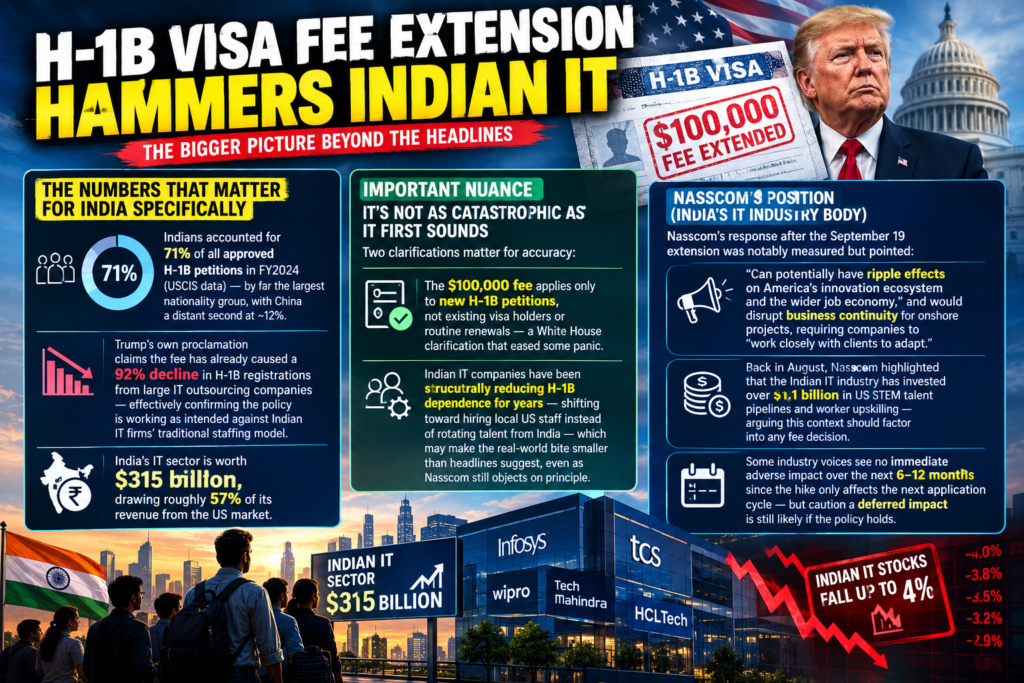
- Indians accounted for 71% of all approved H-1B petitions in FY2024 (USCIS data) — by far the largest nationality group, with China a distant second at ~12%.
- Trump’s own proclamation claims the fee has already caused a 92% decline in H-1B registrations from large IT outsourcing companies — effectively confirming the policy is working as intended against Indian IT firms’ traditional staffing model.
- India’s IT sector is worth $315 billion, drawing roughly 57% of its revenue from the US market.
Important Nuance: It’s Not as Catastrophic as It First Sounds
Two clarifications matter for accuracy:
- The $100,000 fee applies only to new H-1B petitions, not existing visa holders or routine renewals — a White House clarification that came out within hours of the original 2025 announcement and eased some panic.
- Indian IT companies have been structurally reducing H-1B dependence for years — shifting toward hiring local US staff instead of rotating talent from India — which is precisely why Nasscom argues the fee’s real-world bite may be smaller than headlines suggest, even as it still objects on principle.
Nasscom’s Position (India’s IT Industry Body)
Nasscom’s response after the September 19 extension was notably measured but pointed:
- It warned the changes “can potentially have ripple effects on America’s innovation ecosystem and the wider job economy,” and would disrupt business continuity for onshore projects, requiring companies to “work closely with clients to adapt.”
- Back in August, Nasscom highlighted that the Indian IT industry has invested over $1.1 billion in US STEM talent pipelines and worker upskilling — arguing this context should factor into any fee decision.
- Some industry voices have said they see no immediate adverse impact over the next 6–12 months since the hike only affects the next application cycle — but caution a deferred impact is still likely if the policy holds.
The Separate “9-11” Fee Rule — Why It’s the Sneakier Story
This is the part with less press coverage but arguably more direct financial bite: effective September 9, 2026, the expanded Biometric Entry-Exit Fee rule now charges employers $4,000 per H-1B extension and $4,500 per L-1 extension — even for the same employee, same company, just extending an existing visa. Analysts flagged this as the sharper sting for the stock selloff that week, since it converts what was once an occasional cost into a recurring annual line item specifically for firms built around onshore Indian engineers.
Additional Political Layer
Trump also signed an executive order directing federal agencies to apply greater scrutiny to H-1B applications from companies conducting layoffs — a rule that could complicate matters for IT majors simultaneously downsizing in some units while trying to bring in specialized talent elsewhere, adding a compliance headache on top of the direct cost increase.
Bottom Line for Your Segment
This is really a three-layer squeeze on Indian IT: (1) the $100,000 new-application fee, now locked in through 2027, (2) the newer $4,000–$4,500 recurring renewal fee hitting existing staff, and (3) added scrutiny tied to layoffs — landing on a sector already down roughly 24–37% for the year depending on the stock. Nasscom’s own language — “ripple effects,” “business continuity…disrupted” — signals real concern even while downplaying panic.


Spain’s train crash and upcoming election. Spain is dealing with its second deadly train crash this year.

Hong Kong’s Tai Po fire fallout. Leader John Lee apologized

Serbia’s media shake-up. The head of public broadcaster RTS resigned after the student list won an election.

Generation Z Is Killing Fast Fashion in India — And Building Something Far More Beautiful in Its Place

AR Rahman reacts to “anti-national” row over Imtiaz Ali’s Main Vaapas Aaunga

According to Dior Couture, this taboo fashion accessory is back

-
 Entertainment5 hours ago
2026 is a big year at the box office
-
 Entertainment6 hours ago
Ramayana Part 1 arrives this week.
-
 Entertainment6 hours ago
Rajinikanth’s Jailer 2 enters the top 20.
-
 Entertainment5 hours ago
Bigg Boss 20 drama. Manoj Tiwari defended his daughter
-
 Entertainment5 hours ago
Other Diwali releases. Nayanthara’s Mookuthi Amman .